OpenAI engineer accused of using chatbots to plan executive room surveillance
Prosecutors allege Abdulrahman Alfozan used AI tools to schedule meetings and conceal a recording device in a conference room.
Key points
- Federal prosecutors accuse an OpenAI engineer of planting a covert audio recorder in an executive meeting space.
- The suspect allegedly used internal productivity agents and external chatbots to plan the surveillance operation.
- OpenAI states there is no evidence that model weights, source code, or customer data were exfiltrated.
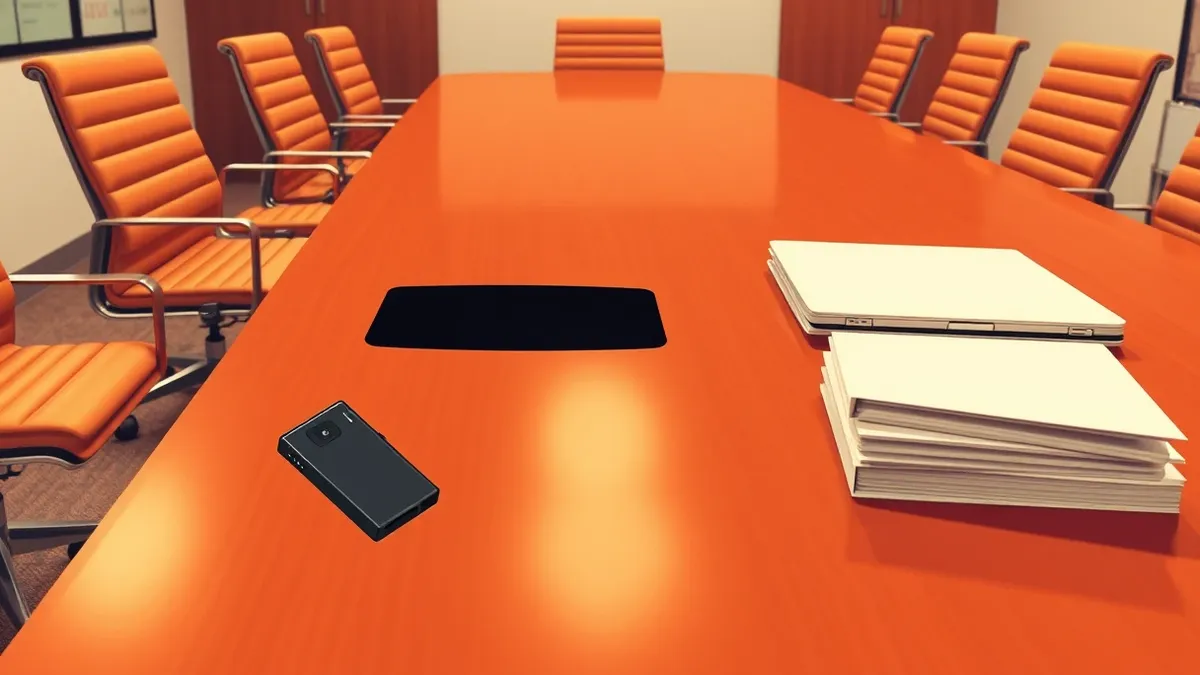
An engineer at OpenAI is accused of concealing an audio recording device within a piece of toilet paper and attaching it behind a monitor in an executive conference room at a San Francisco office, according to a criminal complaint unsealed on Tuesday. The device was discovered during a countersurveillance sweep on September 30.
Root cause
Abdulrahman Alfozan, described by federal prosecutors as a thirty-five-year-old Saudi Arabian national and US permanent resident, allegedly spent several weeks planning the surveillance operation. He reportedly used an unspecified productivity agent and an AI chatbot to assist with the setup. Prosecutors state he queried these tools to learn how to establish a covert listening device.
Attack path
Alfozan allegedly used an internal OpenAI tool to check meeting schedules for the targeted conference room. He also appears to have used a chatbot account linked to his spouse to ask technical questions about setting up the audio recorder. OpenAI’s security team subsequently found an additional recording device in his bag at the office.
Affected versions
This incident involves physical security breaches rather than software version vulnerabilities. The complaint details actions taken by a single employee who joined OpenAI in July 2025. He was terminated last Friday, coinciding with his arrest. No specific software versions or CVE identifiers are associated with this physical intrusion event.
Mitigation
- Conduct regular physical security audits of executive meeting spaces and high-value areas.
- Review access logs for internal tools used to query sensitive scheduling or location data.
- Monitor employee use of internal AI agents for unusual patterns related to security planning.
- Implement stricter bag checks or surveillance protocols for personnel with access to executive zones.
What it means for organisations
Organisations should review how internal AI tools are monitored for misuse in planning physical intrusions. Security teams must assess whether employees can use productivity agents to gather sensitive scheduling data. Leadership should verify that physical access controls align with digital permissions. Incident response plans need to cover scenarios where insiders use AI to facilitate espionage. Cross-functional teams should evaluate if current countersurveillance measures are sufficient for high-risk areas.
Background: AI agents
AI agents matter for security because they move beyond generating text to executing code and accessing systems. This autonomy means a single compromised prompt can trigger cascading failures across your infrastructure, requiring new controls for intent verification and action boundaries rather than just content filtering.
Read the full guide: Why AI Agents Matter for Security: Autonomy Risks
What to do and how to stay safe: OpenAI
- Audit internal AI agent usage logs for queries related to security, surveillance, or sensitive schedules.
- Perform physical inspections of executive conference rooms for unauthorised hardware or hidden devices.
- Review employee access rights to internal scheduling and location tools to limit unnecessary visibility.
- Update insider threat detection policies to include monitoring for AI-assisted planning of physical breaches.
General security guidance from the TechSec Observer newsroom. It is not confirmed advice from the organisations named in this story.
Frequently asked questions
Did the suspect steal any OpenAI source code or data?
OpenAI stated there are no indications that the individual inappropriately accessed or exfiltrated model weights, source code, or customer data.
What charges is the suspect facing?
Alfozan faces one charge of using an electronic device to intercept oral communications, carrying a potential sentence of up to five years in prison.
How was the recording device hidden?
The device was allegedly concealed in toilet paper and inserted into a USB port on the back of a television in the conference room.