Data Breaches
Implement Digital Forensics: A Step-by-Step Guide for Preservation
Evidence integrity fails when you power down a compromised system, as volatile memory contains the only record of active decryption keys and network connections.
Data Breaches coverage from TechSec Observer holds 12 articles, 11 of them reference guides. The newest was published on October 14, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include Have I Been Pwned and NIST Cybersecurity Framework.
Evidence integrity fails when you power down a compromised system, as volatile memory contains the only record of active decryption keys and network connections.
Tax identity theft often manifests as unexpected tax filing rejections or unexplained changes to your direct deposit details rather than visible fraud on bank statements.
Legal compliance officers define retention rules, yet engineering teams control the technical deletion mechanisms that actually enforce them.
Effective data loss prevention rules inspect content patterns rather than file names, ensuring sensitive information is blocked even when users rename files to bypass filters.
Fraudsters assemble real and fake data to create new identities that bypass traditional credit checks and age into legitimate profiles over time.
Data loss prevention stops information leaving your network, but it often blocks legitimate work more frequently than it catches actual theft.
The Federal Bureau of Investigation has charged a specialist in cyber extortion with the crime, shortly after he published a guide on handling such incidents.
Attackers rarely break walls; they wait for you to leave the door open by abusing trusted channels and normalising small data transfers that bypass standard security checks.
Most insider theft is not malicious intent but uncontrolled access, meaning detection relies on behaviour analysis rather than signature matching.
Protecting customer records requires understanding architectural flaws rather than relying on perimeter defences that fail when internal logic is compromised by design.
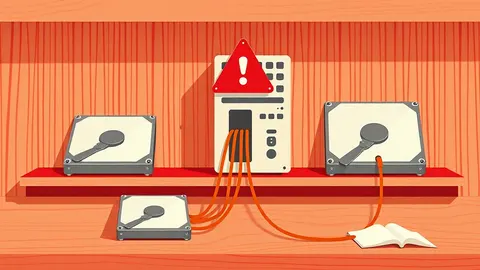
Standard backup configurations often fail because they leave copies connected to the same network, allowing malware to encrypt every version simultaneously.
Small teams fail not from lack of tools, but from ambiguity in decision-making authority during the first hour of an incident.