Privacy & Policy
Checking if your email was in a breach and what happens behind the scenes
Automated breach lookup services match cryptographic hashes of your address against massive public databases of leaked credentials.
Privacy & Policy coverage from TechSec Observer holds 18 articles, 17 of them reference guides. The newest was published on October 19, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include European Commission: Data Protection and NIST Privacy Framework.
Automated breach lookup services match cryptographic hashes of your address against massive public databases of leaked credentials.
True confidentiality requires managing metadata exposure long before the encrypted payload ever reaches the remote recipient.
Adding specific suffixes to your network name stops major mapping services from harvesting your router location without compromising signal quality.
Statistical noise added to datasets prevents identification of individuals while preserving aggregate patterns for public policy and research.
Aliases hide your real address at the protocol level, while forwarding merely routes messages after they arrive, leaving your true identity visible to senders.
The watchdog analysed over 1,000 parliamentary amendments to reveal which legislators support privacy rights and which favour industry loopholes.
Pseudonymization separates identity from utility by replacing direct identifiers with reversible tokens, lowering breach impact while retaining analytical value for research and development.
Aggregators compile public records into searchable profiles, exposing staff details to social engineers without any consent or notification from the individuals involved.
Your documents reveal operational secrets through invisible headers, forcing small teams to adopt rigorous sanitisation workflows to prevent accidental data leaks.
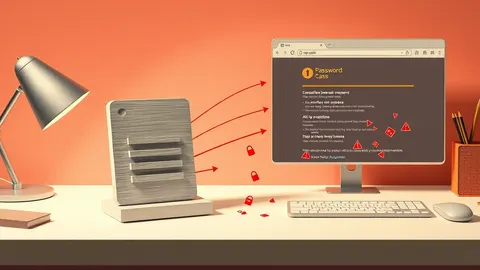
Browser password managers store credentials in the same process as web content, creating a broader attack surface than standalone applications with isolated storage.
Your digital trail is not merely a list of websites you visit; it is a persistent record of your habits, connections, and preferences that persists long after you log off.
Most people-search sites scrape public records, not hacked databases, meaning data minimisation at the source is far more effective than removal requests.
Embedding privacy at the architectural level prevents data leaks that retroactive security patches cannot fix, shifting risk from users to systems.
Legitimate interest allows lawful data processing without consent, but only when your needs do not override the individual's fundamental privacy rights.
Most consent banners fail because they track users before permission is granted, rendering the entire consent mechanism legally void and technically flawed.
Most parental control failures stem from credential sharing, not software limits. The most effective layer is architectural isolation, not content filtering.
Your social media activity builds a profile that persists long after you delete accounts, often revealing more than you intend through metadata and network analysis.
See how privacy browsers isolate sessions, block scripts, and manage cookies to stop behavioural profiling without breaking the web.