Vulnerabilities
SQL Injection Response: Containment, Recovery and Prevention Steps
Restoring service before verifying data integrity often re-exposes the system, turning a contained breach into a persistent backdoor that survives standard patches.
Restoring service before verifying data integrity often re-exposes the system, turning a contained breach into a persistent backdoor that survives standard patches.
Attackers rarely need to read your screen directly; they often capture data through reflected light, camera angles, or by watching your finger movements on a physical keyboard.
Machine learning models detect anomalies by recognising deviations from established baselines, yet they require rigorous data hygiene to avoid amplifying noise into false alarms.
Embedding privacy at the architectural level prevents data leaks that retroactive security patches cannot fix, shifting risk from users to systems.
Protecting customer records requires understanding architectural flaws rather than relying on perimeter defences that fail when internal logic is compromised by design.
Blocking read access to removable media leaves systems vulnerable to power-based attacks that bypass traditional file system controls entirely.
A single typo in a declarative configuration file can expose entire cloud environments, turning automated deployment into a vector for persistent access.
Most AI breaches fail not from code errors, but because teams rebuild trust in compromised models without verifying the integrity of their training data lineage.
Immediate credential rotation prevents lateral movement, but preserving forensic evidence often requires delaying system reboots that would erase memory traces.
Models memorise rare data points during training, allowing attackers to reconstruct sensitive records through carefully crafted queries.
Software composition analysis maps your dependencies but cannot verify how those components interact within your specific runtime environment.
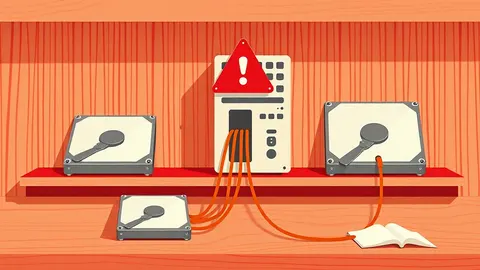
Standard backup configurations often fail because they leave copies connected to the same network, allowing malware to encrypt every version simultaneously.
Systematic testing of AI models reveals hidden failure modes that standard security reviews miss, preventing costly errors before deployment.
Most organisations fail because they measure attack success rather than detection quality, leaving critical blind spots in their monitoring infrastructure.
Small teams fail not from lack of tools, but from ambiguity in decision-making authority during the first hour of an incident.
Signature-based detection offers instant recognition of known threats but fails entirely against new, unrecognised code variants.
Certificate failures often stem from misconfigured chain ordering or hidden intermediate expiry dates rather than the end-entity certificate itself, causing silent trust breaks.
Mobile malware often hides in plain sight by abusing legitimate system permissions, leaving no trace in traditional network logs or file hashes.
Legitimate interest allows lawful data processing without consent, but only when your needs do not override the individual's fundamental privacy rights.
Erasing poisoned data rarely works because the model retains statistical correlations, requiring full retraining from verified sources.
Most consent banners fail because they track users before permission is granted, rendering the entire consent mechanism legally void and technically flawed.
Bluetooth pairing relies on a temporary link key that vanishes after disconnection, leaving long-term bonds vulnerable to replay attacks if not properly managed.
Static rules fail against modern bots because they mimic human behaviour, requiring dynamic validation and behavioural analysis to distinguish legitimate users from automated scripts.
Autonomous agents execute actions without human approval, creating attack surfaces that traditional input validation cannot contain or monitor effectively.